Account Take Over | P1 — Critical
It started off like any other day until I got an unexpected email — an invite to a private bug bounty program. Curious, I jumped in. The…
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/account-take-over-p1-critical-5468ce8218b9?sour … ⌘ Read more
22. How to Get Invites to Private Programs
Unlock the secrets to landing exclusive private program invites and level up your bug bounty journey.
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/22-how-to-get-invites-to-private-programs-9bbb5166 … ⌘ Read more
How to Build a Solar Powered Electric Oven
Image: The insulated solar electric cooker that we build in this manual. Photo by Marie Verdeil. ARTICLE
- Cooking’s high power use
- [How to adapt an electric cooking device to solar power](#ada … ⌘ Read more
Satellite images reveal ancient hunting traps used by South American social groups
Satellite images have revealed an ancient system of elaborate, funnel-shaped mega traps likely built by hunters and pastoralists to catch prey in the high altitudes of northern Chile. ⌘ Read more
How to Assemble an Electric Heating Element from Scratch
Image: A removable heat brick, consisting of a nichrome circuit sandwiched between two identical … ⌘ Read more
21. Tips for Staying Consistent and Avoiding Burnout
What if the secret to lasting success isn’t working harder, but pacing yourself smarter?
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/21-tips-for-staying-consistent-an … ⌘ Read more
Unbelievable Security Hole: JWT Secret in a Series-B Funded Company
It started as a routine penetration test. Little did I know I was about to uncover one of the most basic yet catastrophic security…
[Continue reading on … ⌘ Read more
The $500 Stored XSS Bug in SideFX’s Messaging System
Hacking the Inbox: How a $500 Stored XSS Bug Exposed SideFX’s Messaging Flaw
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/the-500-stored-xss-bug-in-sidefxs-messaging-sys … ⌘ Read more
A Beginner’s Guide to Finding Hidden API Endpoints in JavaScript Files
How to discover what others miss in plain sight
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/a-beginners-guide-to-finding-h … ⌘ Read more
How I Solved TryHackMe Madness CTF: Step-by-Step Beginner-Friendly Walkthrough for 2025
How I Solved “Madness”: An Easy TryHackMe CTF Walkthrough
[Continue reading on InfoSec W … ⌘ Read more
Learn what MITM attack is, and how to identify the footprints of this attack in the network traffic.
How I found Multiple Bugs on CHESS.COM & they refused
I found JS crash, disallowing anyone to view your profile and HTML Injection. But they ignored everything.
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/how-i-found-multiple-bug … ⌘ Read more
CORS Vulnerability with Trusted Insecure Protocols BurpSuite Walkthrough
CORS misconfig + HTTP subdomain XSS analysis showing API key exfiltration, exploit breakdown and remediation.
[Continue reading on InfoSec W … ⌘ Read more
Greta Thunberg and other Global Sumud Flotilla activists used an image of Israeli hostage Evyatar David to illustrate the suffering of Palestinian prisoners incarcerated in Israel. ⌘ Read more
Thunberg shares image of emaciated Israeli hostage in post protesting treatment of Palestinian prisoners ⌘ Read more
**Hidden API Endpoints: The Hacker’s Secret Weapon **
I’m a cybersecurity enthusiast and the writer behind The Hacker’s Log — where I break down how real hackers think, find, and exploit…
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/ … ⌘ Read more
How a Single Signup Flaw Exposed 162,481 User Records
My $8,500 Bug Bounty Story and the Critical Lesson in Authentication
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/how-a-single-signup-flaw-exposed-162-481-user-re … ⌘ Read more
Unlimited access to Docker Hardened Images: Because security should be affordable, always
Every organization we speak with shares the same goal: to deliver software that is secure and free of CVEs. Near-zero CVEs is the ideal state. But achieving that ideal is harder than it sounds, because paradoxes exist at every step. Developers patch quickly, yet new CVEs appear faster than fixes can ship. Organizations standardize on… ⌘ Read more
Chemists create red fluorescent dyes that may enable clearer biomedical imaging
MIT chemists have designed a new type of fluorescent molecule that they hope could be used for applications such as generating clearer images of tumors. ⌘ Read more
Breaking Into HackTheBox: My Journey from Script Kiddie to Root
How I went from copying Pastebin scripts to actually understanding what I was doing — and how you can too.
[Continue reading on InfoSec Write-ups »](https://i … ⌘ Read more
OSINT: Google Dorking Hacks: The X-Ray Vision for Google Search
You type in some keywords, scroll past 10 pages of useless results, and wonder why the internet’s hiding the good stuff. Sound familiar?
[Continue reading on Inf … ⌘ Read more
Mastering Google Dorking: Discovering Website Vulnerabilities
Deep Recon Made Simple: Powering Bug Hunting with Dorking Strategies
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/mastering-google-dorking-d … ⌘ Read more
** Secrets Hackers Don’t Tell: Recon Techniques That Actually Pay**
You see it in the movies: a hacker slams the keyboard, green text scrolls by, and BAM! They’re in. The entire breach takes 90 seconds.
[Continue reading on InfoSe … ⌘ Read more
My Recon Automation Found an Email Confirmation Bypass
How a simple parameter led to a complete authentication bypass
[Continue reading on InfoSec Write-ups »](https://infosecwriteups.com/my-recon-automation-found-an-email-confirmation-byp … ⌘ Read more
Imgur pulls out of UK as data watchdog threatens fine
Article URL: https://www.express.co.uk/news/uk/2115228/image-site-imgur-pulls-out
Comments URL: https://news.ycombinator.com/item?id=45424888
Points: 589
# Comments: 694 ⌘ Read more
Expanding Docker Hardened Images: Secure Helm Charts for Deployments
Development teams are under growing pressure to secure their software supply chains. Teams need trusted images, streamlined deployments, and compliance-ready tooling from partners they can rely on long term. Our customers have made it clear that they’re not just looking for one-off vendors. They’re looking for true security partners across development and deployment. That’s why… ⌘ Read more
DietPi September 2025 Update Brings Faster Backups and Roon Server Early Access
The September 20th release of DietPi v9.17 introduces smaller and more efficient system images, faster backups with reduced disk usage, and a new toggle for Roon Server’s early access builds. The update also addresses SPI bootloader flashing issues on Rockchip devices, improves Raspberry Pi sound card handling, and includes multiple bug fixes across tools and […] ⌘ Read more
Pretty happy with my zs-blog-template starter kit for creating and maintaining your own blog using zs 👌 Demo of what the starter kit looks like here – Basic features include:
- Clean layout & typography
- Chroma code highlighting (aligned to your site palette)
- Accessible copy-code button
- “On this page” collapsible TOC
- RSS, sitemap, robots
- Archives, tags, tag cloud
- Draft support (hidden from lists/feeds)
- Open Graph (OG) & Twitter card meta (default image + per-post overrides)
- Ready-to-use 404 page
As well as custom routes (redirects, rewrites, etc) to support canonical URLs or redirecting old URLs as well as new zs external command capability itself that now lets you do things like:
$ zs newpost
to help kick-start the creation of a new post with all the right “stuff”™ ready to go and then pop open your $EEDITOR 🤞
CNCF’s Helm Project Remains Fully Open Source and Unaffected by Recent Vendor Deprecations
Recently, users may have seen the news about Broadcom (Bitnami) regarding upcoming deprecations of their publicly available container images and Helm Charts. These changes, which will take effect by September 29, 2025, mark a shift to… ⌘ Read more
ProcessOne: Why Europe’s ‘Chat Control’ Proposal Will Cripple European Communication Industry While Failing to Protect Children
On October 14th, the European Concil will vote on a regulation that … ⌘ Read more
Kaidan: Kaidan 0.13.0: Multi-Account Support and Secure Password Storage
Kaidan 0.13.0 is out now!
And it comes with a bunch of shiny new features.
Most of the work has been … ⌘ Read more
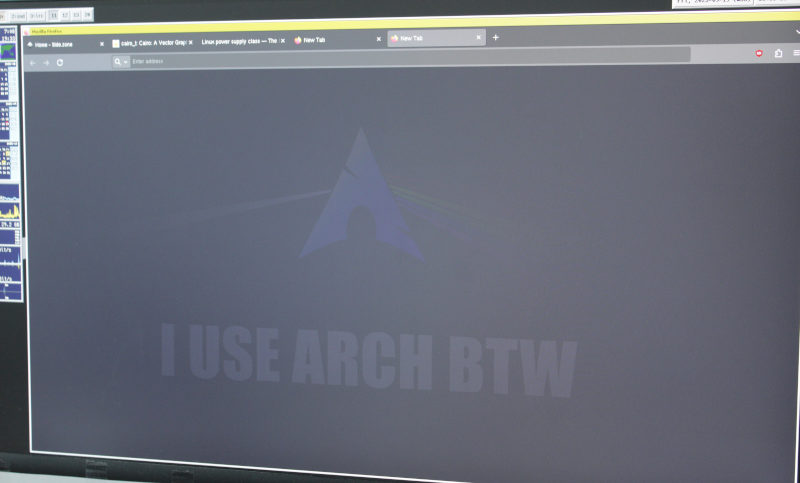
Severe but funny burn-ins on my TFT again:
https://movq.de/v/9df0437d27/MVI_8891.MOV.mp4
Now everything looks like it has that silly slogan as a background image:
Working on a project that does Augmented Reality and computer vision object detection and QR code and image recognition inside a Web application. Pretty neat what can be done today with a few thousand lines of JavaScript.
↳
In-reply-to
»
added opengraph to my blog :D https://bubblegum.girlonthemoon.xyz/articles/underground-soundcloud-remixes
⤋ Read More
The image needs to be an absolute URL, and some tags are missing. Almost there!
↳
In-reply-to
»
Well, that was fascinating: https://www.youtube.com/watch?v=LxNq8zOEbM8
⤋ Read More
@movq@www.uninformativ.de Interesting, yes. I didn’t know that.
No AI being used is really great. However, the same clips shown over and over again and some images being mirrored was quite annoying to me. Also, there were some quite terrible computer animations and sometimes the narration and picture didn’t match at all. Talking about the medieval period and then showing an image from the 18th hundred or so. What the heck?
These production issues made me sceptical pretty much early on. So I quickly crosschecked Wikipedia. But it seems spot on from what I’ve read. Very good. Also, the narrator’s voice was really nice to listen to.
Eels are fascinating creatures. :-)
↳
In-reply-to
»
The original twt is unavailable. It may have been edited or deleted, or is from an unknown or muted feed.
⤋ Read More
@eric@itsericwoodward.com Hmm, the images are all 404ing. Also, I reckon that lots of code blocks are broken, too.
The XMPP Standards Foundation: The XMPP Newsletter August 2025
XMPP Newsletter Banner
Welcome to the XMPP Newsletter, great to have you here again!
This issue covers the month of August 2025.
Like this newsletter, many projects and their efforts in the XMPP community are a result of people’s voluntary work. If you are happy with the services and software you may be using, please consider saying thanks or help these proj … ⌘ Read more
ProcessOne: Spotify’s Direct Messaging Gambit
Last week, Spotify quietly launched direct messaging across its platform in selected areas, allowing users to share tracks and playlists through private conversations within the app. The feature was rolled out with mini … ⌘ Read more
↳
In-reply-to
»
This is something that @kat might enjoy:
⤋ Read More
@movq@www.uninformativ.de Hahaha, great idea! :-D I never saw the Epson Image Scan logo before.